CMMC Gap Assessment
Find and Fix CMMC Compliance Gaps Before Your Assessment
Preparing for Cybersecurity Maturity Model Certification (CMMC) can be challenging, especially when you aren’t sure where your organization currently stands. A CMMC gap assessment from WingSwept helps you identify weaknesses in your cybersecurity environment, policies, procedures, and documentation so you can build a clear path toward compliance. Whether you are pursuing a Department of Defense (DoD) contract, responding to requirements from a prime contractor, or trying to improve a low SPRS score, WingSwept can help you understand what needs to be addressed and what to do next.
Know where you stand. Understand what needs to change. Build your roadmap to CMMC compliance.
What Is a CMMC Gap Assessment?
A CMMC gap assessment compares your organization’s existing cybersecurity practices against the CMMC requirements that apply to your business.
For organizations preparing for CMMC Level 2, this means evaluating how your organization protects Controlled Unclassified Information (CUI) and identifying gaps related to the applicable NIST SP 800-171 security requirements.
Our assessment can help answer important questions, including:
- Which CMMC requirements are we already meeting?
- Where are our most significant compliance gaps?
- Are our cybersecurity policies and procedures sufficient?
- Are we properly protecting CUI?
- What technical improvements do we need to make?
- What should we prioritize first?
- Would a CMMC enclave help reduce our compliance scope?
- What will it realistically take to prepare for CMMC
Instead of guessing about your readiness, you receive a clearer understanding of your current position and the work ahead.

Identify Problems Before They Impact Your DoD Opportunities
For defense contractors and subcontractors, CMMC compliance can have a direct impact on the ability to pursue and maintain DoD business.
Waiting until a contract opportunity or assessment is approaching can leave your organization scrambling to implement security controls, update policies, collect documentation, and resolve IT problems.
A CMMC readiness assessment helps uncover these issues earlier.
It can also give leadership greater insight into the potential cost and operational impact of achieving compliance. Rather than approaching CMMC as one large, uncertain project, your organization can prioritize improvements and develop a phased plan.
What Does Your Gap Assessment Cover?
CMMC compliance requires more than cybersecurity software. Your technology, documentation, policies, processes, and employees all contribute to your compliance posture. Depending on your organization and its requirements, WingSwept can evaluate areas including:
- IT systems and cybersecurity controls
- CUI environment and scope
- Access and authentication practices
- Security policies and procedures
- Existing NIST SP 800-171 documentation
- System Security Plan (SSP) documentation
- Existing Plan of Action and Milestones (POA&M)
- Security practices and supporting evidence
- Opportunities for environment segmentation
- Areas requiring technical or procedural remediation
After identifying your gaps, we help turn those findings into a practical remediation roadmap.
More Than a CMMC Checklist
Finding compliance gaps is only the beginning.
WingSwept provides technical and policy support before and after your CMMC assessment to help your organization address the issues that have been identified.
Your path may include technical remediation, policy development, documentation updates, CUI scoping, cybersecurity improvements, employee process changes, or the creation of a dedicated CMMC enclave.
Our goal is to establish realistic, achievable steps toward compliance, not simply provide a report and leave you to figure out the rest.
Why Choose WingSwept for Your CMMC Gap Assessment?
WingSwept understands the CMMC process firsthand. We are a Managed Service Provider serving defense contractors, and we are also a government contractor ourselves. WingSwept has successfully completed a CMMC Level 2 assessment and is a Cyber AB Registered Practitioner Organization (RPO).
That experience allows our team to understand both sides of CMMC compliance: the policies and documentation required to support compliance and the technical environment needed to protect sensitive information.
Whether you are just beginning your CMMC journey or need help resolving existing compliance gaps, WingSwept can help you understand where you stand and develop a practical path forward.
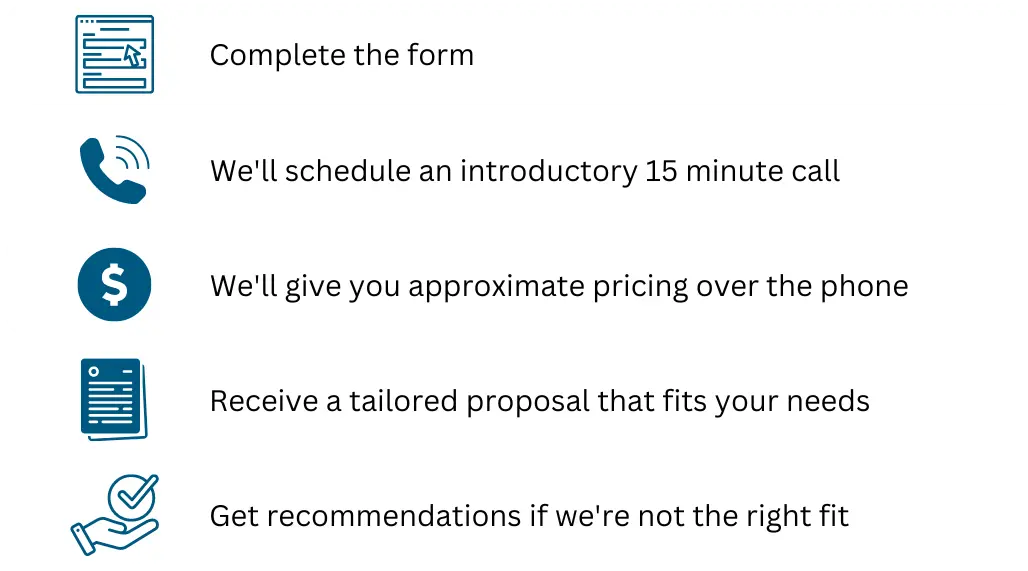
What Happens Next?
Don’t wait until a contract opportunity or assessment puts your organization under pressure. Find out where your CMMC compliance gaps are now and create a plan to address them.
Talk with WingSwept about a CMMC gap assessment today.